Future-Proofing Enterprise Edges: Why Nairobi Businesses are Migrating to FortiGate G-Series Firewalls
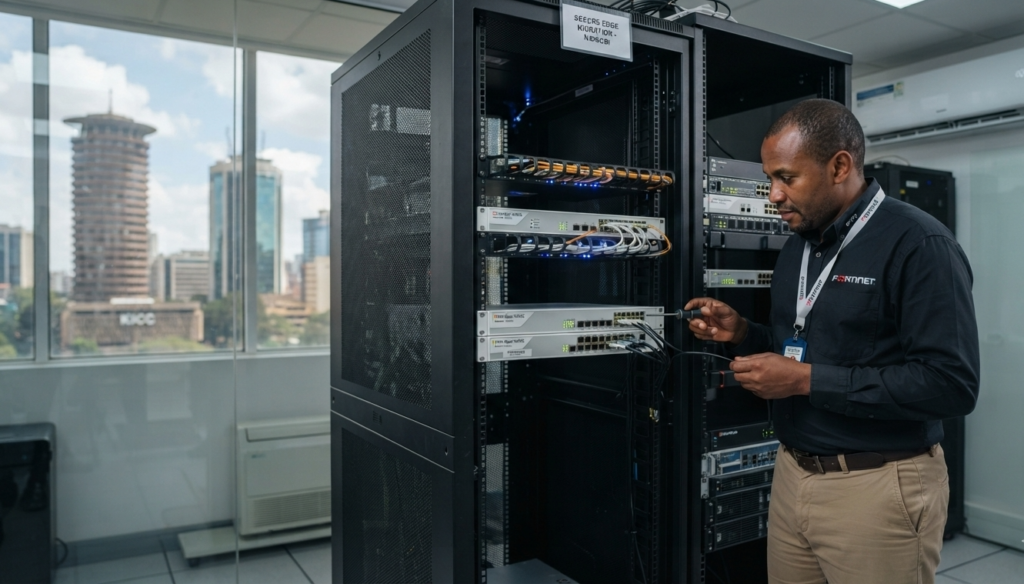
The Processing Breakthrough: Purpose-Built Security ASICs
Purpose-Built Security ASICs
The foundational limitation of standard commercial firewalls is their dependency on off-the-shelf CPUs to manage security processing. When intensive operations like deep SSL/TLS decryption and real-time Intrusion Prevention (IPS) are enabled, performance typically plummets.The FortiGate G-Series eliminates this issue entirely by utilizing Fortinet’s proprietary SP5 (Security Processor 5) ASIC architecture. Instead of processing traffic through generic software layers, the SP5 runs security compute functions inline via specialized hardware. This yields distinct structural benefits:Accelerated Threat Protection: Delivers up to 2x to 3x the active threat protection throughput of previous-generation appliances.Ultra-Low Latency Inspection: Inspects encrypted traffic flows at wire-speed without degrading corporate application performance.Optimal Energy Efficiency: Drastically lowers power consumption metrics within compact branch network closets.
Enterprise Features Redefining Branch Operations
1. AI-Powered FortiGuard Services
Backed by global real-time threat intelligence from FortiGuard Labs, G-Series appliances leverage embedded machine learning. They dynamically detect and block zero-day exploits, coordinate inline malware prevention, and filter advanced web threats before they can bypass your perimeter.
2. Integrated Secure SD-WAN
Say goodbye to expensive, rigid MPLS links. FortiGate firewalls natively incorporate sophisticated, application-aware SD-WAN path selection. This allows your branch operations to securely route critical traffic across multiple local internet lines, automatically switching paths to avoid localized ISP dropouts.
3. Dynamic Security Fabric Expansion
Through FortiLink technology, your firewall functions as the central nervous system for your entire office space. It securely interfaces with access layer hardware like the FortiSwitch 148F-POE, allowing your central engineering team to monitor ports, assign VLANs, and quarantine untrusted devices directly from a unified dashboard.
Deploying Next-Gen Firewalls Seamlessly with Networks Kenya
- Tailored Topology Assessments: We audit your existing traffic trends to provision the exact FortiGate model required to maintain optimal compute overhead.
- Zero-Downtime Migration Execution: We pre-configure policies, security profiles, and interface states to ensure seamless switchovers with minimal disruption to daily business flow.
- Localized Lifetime Support: Benefit from responsive, regional technical expertise optimized to troubleshoot local connectivity anomalies across East Africa.